Remote and hybrid work
Onboarding a hire you'll never meet in person means proving identity to an I-9 standard without a desk to sit them at - and doing it in hours, not the first week.
Issuance with Credence lets enterprises issue a single verified workforce credential that onboards a new hire, replaces the password at login, and opens the door to the building - all from the phone the employee already carries. One identity, issued once, trusted across every system.
ISO/IEC 18013-5 · W3C VC 2.0 · OpenID4VCI · FIDO-aligned · FIPS 140-3 Level 3 · ISO 27001
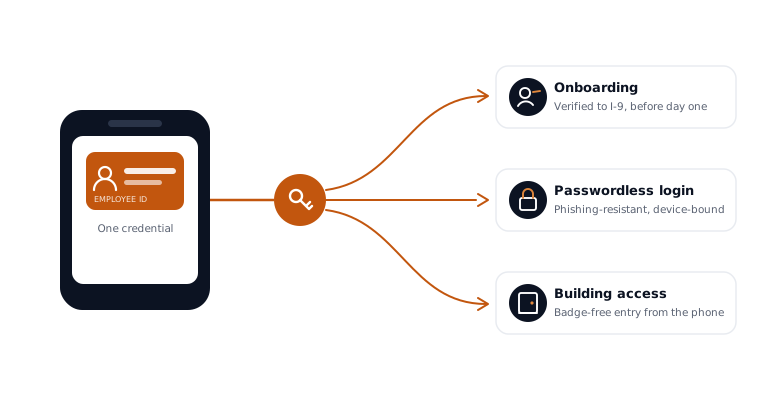
The old enterprise ran on a badge and a password. Neither holds up anymore. Work happens remotely, contractors come and go, and the attack that lands hardest is the one that walks straight through the front door with stolen credentials.
Three pressures are forcing consolidation.
Onboarding a hire you'll never meet in person means proving identity to an I-9 standard without a desk to sit them at - and doing it in hours, not the first week.
Phished passwords and cloned badges are the leading way attackers get in. Every static secret is a liability; identity that can't be phished is the only durable fix.
Temps, vendors, and cross-site staff need access that's provisioned fast and revoked the instant they leave - something plastic badges and manual offboarding never deliver cleanly.
The status quo makes every enterprise run the same identity three times over.
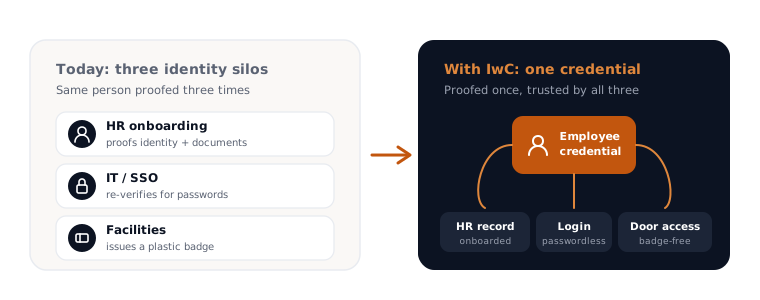
HR verifies a new hire's identity and documents, then hands nothing reusable to IT or facilities - who each re-verify or simply trust on faith.
Static secrets are the softest target in the enterprise. Resets cost the help desk real money, and a single phished credential can open the whole network.
Physical access cards are easy to clone, slow to issue, and routinely walk out the door with departing staff - leaving access open long after someone's gone.
IwC collapses onboarding, logical access, and physical access onto a single verified credential.
Proof a new hire to an I-9 standard remotely - documents, face match, liveness - and issue a workforce credential before their first morning starts.
The credential authenticates the employee to company systems with a device-bound key that can't be phished, cloned, or reused on another device.
The same credential grants physical entry - no plastic badge to issue, lose, or clone. Revoke it once and both network and building access close together.
Run workforce issuance and verification from one platform, backed by open APIs that slot into the identity stack you already have.
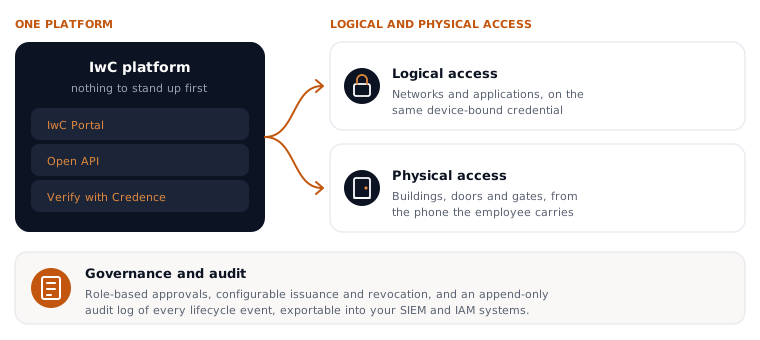
The enterprise is both the issuer and the biggest beneficiary - every credential it issues to its own workforce comes straight back as reduced cost and risk.
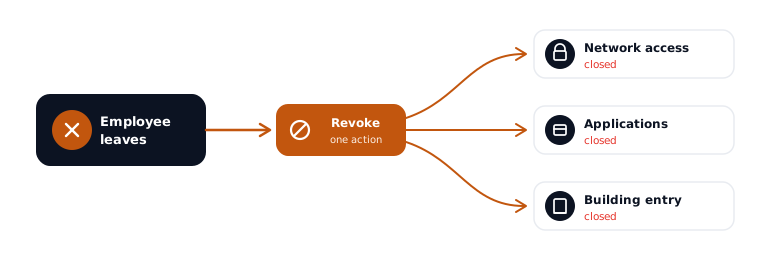
Issue a workforce credential at onboarding and it flows into logical and physical access with no re-provisioning - three systems collapsed into one.
Device-bound, phishing-resistant credentials remove the passwords and cloned badges that most breaches rely on.
Revoke the credential and network access, application access, and building entry all close in the same moment - no orphaned accounts, no active badges in a drawer.
Issue time-boxed credentials to vendors and temps that expire on their own, and to cross-site staff who carry one credential valid at every location.
Enterprises issue several workforce credential types on IwC - each proofed and signed the same way.
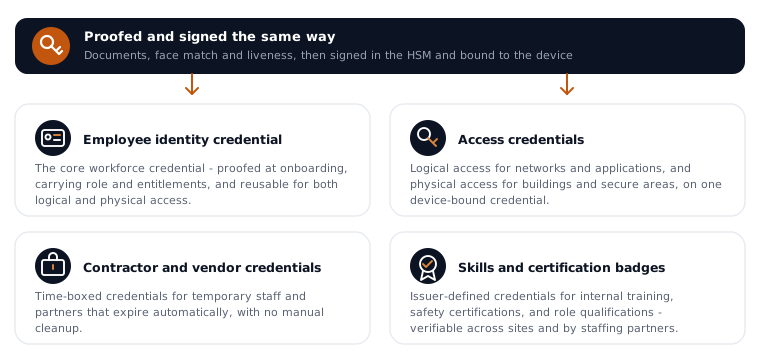
Proof a worker once; the credential carries them through onboarding, login, and entry.
Because IwC issues over OpenID4VCI in both ISO 18013-5 and W3C VC 2.0 formats, the credential works with any conformant wallet, verifier, and access system - not just tools carrying our name.
IwC gives enterprises the tools to move faster while closing the gaps attackers exploit. Employees carry one credential; IT and facilities trust the same verified identity.
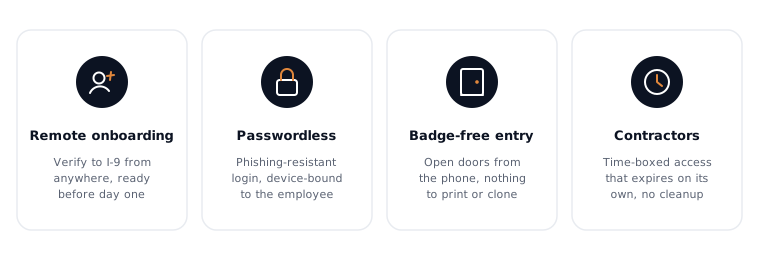
Remote onboarding to an I-9 standard means a verified credential is ready before the first shift - no first-week identity backlog.
Phishing-resistant, device-bound login removes the single most exploited weakness in the enterprise.
Building entry from the phone means nothing to print, clone, or forget at home.
Cross-site and hybrid staff carry one credential valid everywhere they work.
A single revocation closes network and building access together, the moment someone leaves.
Selective disclosure means a door reader confirms entitlement without pulling the employee's full record.
IwC is built by Credence ID, an ISO 27001-certified organization with digital identity and biometric technology deployed in the field across more than fifteen countries, on cloud infrastructure that meets regulated-industry requirements.
Working with Credence ID, your enterprise gets a standards-based credential platform - onboarding, logical access, and physical access on one identity - backed by proven technology, flexible hosting, and expert support. Get in touch to learn more or to start a pilot.
Issuance with Credence - Issue once. Trust everywhere. Manage for life.